SD-WAN and SASE shortlist builder
SD-WAN vendors compared (2026)
Compare public provider evidence in alphabetical order. Publish a verified project to unlock computed fit and rankings.
Provider evidence
Provider, product and differentiator
- Aryaka (AI>Observe, AI>Secure, Aryaka Cyber Threat Research Lab (CTRL), Aryaka Network Access Point (ANAP)): Unified SASE delivered as a managed service from end to end, including the private global core network and WAN optimisation.
- Barracuda SecureEdge (Barracuda SecureEdge, Barracuda SecureEdge Access, BarracudaONE, Secure Edge Manager): Barracuda Networks is a long-established cybersecurity company - founded 2003, initially focused on spam and virus firewalls - that has changed ownership twice in the past decade without ever settling into a stable, single corporate structure: it went public in 2013, was taken private by Thoma Bravo in 2018 for $1.6 billion, and was acquired again by KKR in 2022. SecureEdge, launched in 2023, is Barracuda’s single-vendor SASE platform, integrating Secure SD-WAN, Firewall-as-a-Service, ZTNA and Secure Web Gateway, and it now sits within Barracuda’s broader BarracudaONE umbrella alongside the company’s much older, well-established email, data, and application-protection product lines.
- Cato Networks (Cato Browser Extension, Cato Client, Cato DEM, Cato EPP/EDR): Single converged platform with no policy or log fragmentation across SD-WAN and security functions.
- Check Point (AI Network Firewall / AI Defence Plane, CASB, Check Point Infinity Architecture, Check Point SASE Platform): Harmony SASE combines Check Point security heritage with cloud-delivered SASE and optimised SD-WAN performance.
- Cisco (Cisco AI Defence, Cisco Catalyst SD-WAN, Cisco Duo, Cisco ISE): Broadest platform portfolio in the category, covering Catalyst SD-WAN for enterprise WAN, Meraki MX for cloud-managed branch, and Cisco Secure Access for converged SASE delivery.
- Ericsson Cradlepoint (NetCloud Federal, NetCloud Manager, NetCloud Perimeter, NetCloud Private Networks): Wireless-first branch architecture from Ericsson with deep 5G expertise; NetCloud provides cellular-centric SD-WAN management.
- Forcepoint (AI Mesh / Getvisibility, ARIA, Field Programmable SASE Logic (FPSL), FlexEdge Secure SD-WAN): FlexEdge Secure SD-WAN combines secure SD-WAN with strong DLP and data security heritage from the wider Forcepoint portfolio.
- HPE Aruba EdgeConnect (Cloud Intelligence, EdgeConnect Orchestrator, First-Packet iQ, HPE Aruba Networking Central): EdgeConnect SD-WAN (acquired with Silver Peak) is positioned as the foundation for single-vendor SASE alongside Aruba SSE.
- Juniper Networks (Juniper AI-Native SD-WAN, Juniper Mist AI / Marvis AI, Juniper Secure Edge, Managed SD-WAN): Mist AI delivers WAN Assurance, providing AI-driven monitoring and troubleshooting at the WAN edge that few competitors match.
- Lumen (Black Lotus Labs, Lumen Managed SASE Solutions, Lumen SASE with Versa, Lumen SD-WAN with Versa Networks): Fully managed or co-managed SD-WAN with strong NaaS positioning and integrated network services.
- Netskope (Borderless SD-WAN, Cloud Confidence Index (CCI), Netskope Cloud Exchange (CE), Netskope One): Strong CASB heritage; widely recognised as a leading SSE vendor for SaaS-heavy environments.
- Open Systems (MDR+ (Managed Detection and Response), Managed SD-WAN / Secure SD-WAN, Managed, Universal SSE, Mission Control): Open Systems founded in 1990 in Basel, Switzerland, more than three decades before the SASE category itself existed, originally as a managed security service provider before evolving its platform into what it now markets as native, managed SASE Experience. The company’s ownership history took a distinctive turn in 2023: after a period under the European private-equity firm EQT, Open Systems was acquired by Swiss Post - Switzerland’s state-backed national postal and logistics institution - a materially different kind of owner from the venture-capital or private-equity structures behind most other vendors in this category.
- Palo Alto Networks Prisma SASE (ADEM, AI Access Security, Enterprise DLP, Precision AI / Strata Copilot): Prisma SASE converges SD-WAN, cloud-delivered security, and digital experience management (ADEM) under a single platform identity.
- VeloCloud (Arista AVA, Edge Threat Management (ETM), SSE partner integrations, VeloCloud Orchestrator): VeloCloud was an early SD-WAN platform with strong cloud-delivered gateway architecture; now under Arista following the 2025 acquisition.
- Versa Networks (Inbound SSE, Secure Enterprise Browser, VOS, Versa Analytics): Multi-tenancy from the ground up, making Versa a common choice for service providers and carriers building managed SD-WAN and SASE platforms.
- Zscaler (AI Security / GenAI Security, Data Fabric for Security, Risk360, Zero Trust Branch): Category leader in SSE with ZIA, ZPA and ZDX; widely adopted as the security layer in best-of-breed SASE architectures.
Comparison summary
Evidence for SD-WAN vendors at a glance
| Provider | Type | Products | Best suited to | Main strength | Confirm through RFP | Reviewed |
|---|---|---|---|---|---|---|
| Aryaka | technology vendor | AI>Observe, AI>Secure, Aryaka Cyber Threat Research Lab (CTRL), Aryaka Network Access Point (ANAP) | Global enterprises wanting SASE delivered as a fully managed service rather than as DIY platform plus tools. | Unified SASE delivered as a managed service from end to end, including the private global core network and WAN optimisation. | Fully managed service | 2026-09-01 |
| Barracuda SecureEdge | technology vendor | Barracuda SecureEdge, Barracuda SecureEdge Access, BarracudaONE, Secure Edge Manager | Barracuda Networks is a long-established cybersecurity company - founded 2003, initially focused on spam and virus firewalls - that has changed ownership twice in the past decade without ever settling into a stable, single corporate structure: it went public in 2013, was taken private by Thoma Bravo in 2018 for $1.6 billion, and was acquired again by KKR in 2022. SecureEdge, launched in 2023, is Barracuda’s single-vendor SASE platform, integrating Secure SD-WAN, Firewall-as-a-Service, ZTNA and Secure Web Gateway, and it now sits within Barracuda’s broader BarracudaONE umbrella alongside the company’s much older, well-established email, data, and application-protection product lines. | Barracuda Networks is a long-established cybersecurity company - founded 2003, initially focused on spam and virus firewalls - that has changed ownership twice in the past decade without ever settling into a stable, single corporate structure: it went public in 2013, was taken private by Thoma Bravo in 2018 for $1.6 billion, and was acquired again by KKR in 2022. SecureEdge, launched in 2023, is Barracuda’s single-vendor SASE platform, integrating Secure SD-WAN, Firewall-as-a-Service, ZTNA and Secure Web Gateway, and it now sits within Barracuda’s broader BarracudaONE umbrella alongside the company’s much older, well-established email, data, and application-protection product lines. | Fully managed service | 2026-09-01 |
| Cato Networks | technology vendor | Cato Browser Extension, Cato Client, Cato DEM, Cato EPP/EDR | Mid-market and enterprise buyers consolidating SD-WAN and SASE on one platform from a single vendor. | Single converged platform with no policy or log fragmentation across SD-WAN and security functions. | Fully managed service | 2026-09-01 |
| Check Point | technology vendor | AI Network Firewall / AI Defence Plane, CASB, Check Point Infinity Architecture, Check Point SASE Platform | Existing Check Point customers extending firewall investment into SD-WAN and SASE. | Harmony SASE combines Check Point security heritage with cloud-delivered SASE and optimised SD-WAN performance. | Fully managed service | 2026-09-01 |
| Cisco | technology vendor | Cisco AI Defence, Cisco Catalyst SD-WAN, Cisco Duo, Cisco ISE | Enterprises already standardised on Cisco networking who want platform consistency from LAN through WAN to security. | Broadest platform portfolio in the category, covering Catalyst SD-WAN for enterprise WAN, Meraki MX for cloud-managed branch, and Cisco Secure Access for converged SASE delivery. | Fully managed service | 2026-09-01 |
| Ericsson Cradlepoint | technology vendor / carrier network provider | NetCloud Federal, NetCloud Manager, NetCloud Perimeter, NetCloud Private Networks | Distributed enterprises with strong cellular/5G access strategy (retail, logistics, transport, public sector). | Wireless-first branch architecture from Ericsson with deep 5G expertise; NetCloud provides cellular-centric SD-WAN management. | Co-managed service | 2026-09-01 |
| Forcepoint | technology vendor | AI Mesh / Getvisibility, ARIA, Field Programmable SASE Logic (FPSL), FlexEdge Secure SD-WAN | Enterprises with strong data protection and DLP requirements (regulated industries, government). | FlexEdge Secure SD-WAN combines secure SD-WAN with strong DLP and data security heritage from the wider Forcepoint portfolio. | Fully managed service | 2026-09-01 |
| HPE Aruba EdgeConnect | technology vendor | Cloud Intelligence, EdgeConnect Orchestrator, First-Packet iQ, HPE Aruba Networking Central | Enterprises already running Aruba LAN/Wi-Fi who want WAN and SASE under the same operational tooling. | EdgeConnect SD-WAN (acquired with Silver Peak) is positioned as the foundation for single-vendor SASE alongside Aruba SSE. | Fully managed service | 2026-09-01 |
| Juniper Networks | technology vendor | Juniper AI-Native SD-WAN, Juniper Mist AI / Marvis AI, Juniper Secure Edge, Managed SD-WAN | Enterprises already running Mist for Wi-Fi or access who want unified AI-driven operations across WAN and LAN. | Mist AI delivers WAN Assurance, providing AI-driven monitoring and troubleshooting at the WAN edge that few competitors match. | Fully managed service | 2026-09-01 |
| Lumen | technology vendor / managed service provider / carrier network provider | Black Lotus Labs, Lumen Managed SASE Solutions, Lumen SASE with Versa, Lumen SD-WAN with Versa Networks | North American enterprises wanting integrated managed SD-WAN, access and broader network services from one provider. | Fully managed or co-managed SD-WAN with strong NaaS positioning and integrated network services. | Multi-tenant MSP / white-label support | 2026-09-01 |
| Netskope | technology vendor | Borderless SD-WAN, Cloud Confidence Index (CCI), Netskope Cloud Exchange (CE), Netskope One | Enterprises with deep SaaS adoption where CASB and DLP are top procurement priorities. | Strong CASB heritage; widely recognised as a leading SSE vendor for SaaS-heavy environments. | Fully managed service | 2026-09-01 |
| Open Systems | technology vendor / managed service provider | MDR+ (Managed Detection and Response), Managed SD-WAN / Secure SD-WAN, Managed, Universal SSE, Mission Control | Open Systems founded in 1990 in Basel, Switzerland, more than three decades before the SASE category itself existed, originally as a managed security service provider before evolving its platform into what it now markets as native, managed SASE Experience. The company’s ownership history took a distinctive turn in 2023: after a period under the European private-equity firm EQT, Open Systems was acquired by Swiss Post - Switzerland’s state-backed national postal and logistics institution - a materially different kind of owner from the venture-capital or private-equity structures behind most other vendors in this category. | Open Systems founded in 1990 in Basel, Switzerland, more than three decades before the SASE category itself existed, originally as a managed security service provider before evolving its platform into what it now markets as native, managed SASE Experience. The company’s ownership history took a distinctive turn in 2023: after a period under the European private-equity firm EQT, Open Systems was acquired by Swiss Post - Switzerland’s state-backed national postal and logistics institution - a materially different kind of owner from the venture-capital or private-equity structures behind most other vendors in this category. | Multi-tenant MSP / white-label support | 2026-09-01 |
| Palo Alto Networks Prisma SASE | technology vendor | ADEM, AI Access Security, Enterprise DLP, Precision AI / Strata Copilot | Enterprises with mature security operations that want SASE built around a leading security platform rather than a security layer on top of an SD-WAN platform. | Prisma SASE converges SD-WAN, cloud-delivered security, and digital experience management (ADEM) under a single platform identity. | Fully managed service | 2026-09-01 |
| VeloCloud | technology vendor | Arista AVA, Edge Threat Management (ETM), SSE partner integrations, VeloCloud Orchestrator | Enterprises consuming VeloCloud through a managed service provider (Vodafone UK, others). | VeloCloud was an early SD-WAN platform with strong cloud-delivered gateway architecture; now under Arista following the 2025 acquisition. | Fully managed service | 2026-09-01 |
| Versa Networks | technology vendor | Inbound SSE, Secure Enterprise Browser, VOS, Versa Analytics | Service providers, carriers and MSPs building white-label managed SD-WAN or SASE services. | Multi-tenancy from the ground up, making Versa a common choice for service providers and carriers building managed SD-WAN and SASE platforms. | Fully managed service | 2026-09-01 |
| Zscaler | technology vendor | AI Security / GenAI Security, Data Fabric for Security, Risk360, Zero Trust Branch | Enterprises selecting best-of-breed SSE alongside a separate SD-WAN platform. | Category leader in SSE with ZIA, ZPA and ZDX; widely adopted as the security layer in best-of-breed SASE architectures. | Fully managed service | 2026-09-01 |
The table uses governed provider records. Unknown evidence is shown as a point to confirm, not a negative score.
Short answer: compare 30 SD-WAN providers, SD-WAN vendors, SASE providers, carriers and managed services using one governed research dataset. Compare named providers feature by feature or open their evidence profiles. Publish a short anonymous project to unlock personalised matching and supplier responses.
- Free for buyers
- No sales calls until you reply
- Pricing private to you
- No obligation to award
Written and reviewed by the Netify research team. The governed provider records were last updated on 2026-09-01. Comparison contract governed-shortlist/1.0.0. To act on a shortlist, describe the project once at the Netify RFP Builder, review and publish an anonymous brief or RFP to invite supplier responses, then compare structured responses, with pricing kept private to the buyer. Read and cite the research method.
2026 market answer
SD-WAN vendors compared
Compare public provider evidence in alphabetical order. Publish a verified project to unlock computed fit and rankings.
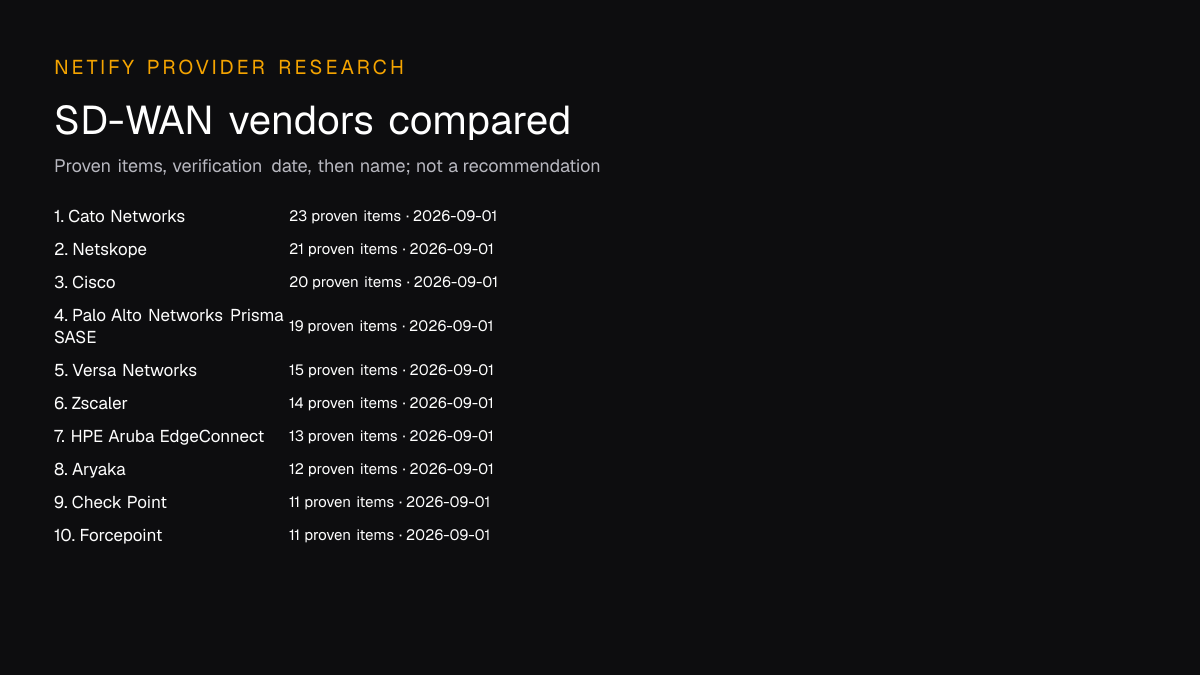
16 providers in this evidence view. Reviewed 2026-09-01. View contract shortlist-market-view/1.0.0.
Ranked shortlists
Pre-built rankings by sector, size and priority
Definitions
The 40 capabilities, defined
Every provider is graded against the same 40 capabilities. One sentence on what each row measures; grades reflect public evidence, so always confirm via RFP.
Service delivery and operating model
8 capabilities
- Fully managed service.
- The provider designs, deploys, monitors, changes, supports and reports on the service end to end, so the customer sets policy and outcomes rather than running day-to-day operations.
- DIY / self-managed model.
- The customer's own team operates the platform directly, owning the controller, policies, updates and incident response.
- Co-managed service.
- Responsibility is shared: the provider runs the platform and support while the customer retains selected policy and change rights.
- Multi-tenant MSP / white-label support.
- The platform supports tenant isolation, delegated administration, branded portals and templates, so managed service providers can operate it for many customers under their own brand.
- Professional services and migration support.
- Structured design and migration services are available, covering discovery, pilots, staging, migration runbooks, rollback plans and training.
- Last-mile circuit management.
- The provider sources, monitors and supports the underlay access circuits at each site, across broadband, dedicated internet access, LTE and 5G, MPLS and cross-connects, giving one accountable party for connectivity and overlay together.
- Lifecycle management.
- Hardware replacement, firmware upgrades, patching, renewals and end-of-life planning are handled as part of the service.
- Flexible commercial model.
- Pricing can be structured in more than one way, such as per site, per user, per bandwidth, consumption-based or as NaaS, with terms that adapt to the buyer's estate.
Network architecture and transport
10 capabilities
- Encrypted overlay fabric.
- Site and user traffic runs through secure tunnels built over any underlying transport, including broadband, dedicated internet, MPLS, LTE and 5G or satellite, keeping data protected across mixed networks.
- Dynamic path selection.
- The platform routes traffic in real time based on measured latency, jitter, packet loss and policy, steering around brownouts without manual intervention.
- Active-active link utilisation.
- All available links carry traffic concurrently rather than one sitting idle as passive backup, increasing usable capacity and smoothing failover.
- Application-aware routing.
- Traffic is identified at application level and routed by per-application policy, so business-critical applications such as UCaaS and ERP take priority.
- QoS and traffic shaping.
- Bandwidth can be prioritised, reserved and policed per application or traffic class, protecting voice, video and critical traffic under congestion.
- Packet loss remediation.
- Techniques such as forward error correction, packet duplication, jitter buffering and TCP optimisation repair or mask loss on poor-quality links, keeping real-time applications usable.
- Local internet breakout.
- Internet-bound traffic exits securely and directly from the branch rather than being backhauled through a central data centre, reducing latency for cloud and SaaS traffic.
- MPLS coexistence and migration.
- Existing MPLS circuits can run alongside internet and cellular transport during a phased migration, so estates move site by site without a risky single cutover.
- Cellular and 5G support.
- 4G and 5G connections are supported as primary or failover transport, with integrated or external modems, SIM management and signal monitoring.
- Cloud on-ramp.
- Connectivity into cloud platforms such as AWS, Microsoft Azure, Google Cloud and Oracle, and interconnect fabrics such as Equinix and Megaport, is automated and simplified rather than hand-built per cloud.
Gateway, PoP and backbone design
8 capabilities
- Public cloud gateways.
- The vendor operates shared gateways and points of presence that deliver SaaS optimisation, remote access or security enforcement as a cloud service; this measures the vendor's own service infrastructure, distinct from dedicated private PoPs.
- Private PoPs / dedicated PoPs.
- Points of presence can be supplied as customer-hosted, dedicated or sovereign deployments rather than only the provider's shared multi-tenant locations.
- Private global backbone.
- Traffic between regions rides a backbone owned or controlled by the vendor rather than the public internet, giving predictable latency and loss between PoPs.
- Regional breakout and data residency.
- Traffic can be pinned to chosen countries, regions or approved inspection locations, supporting data residency and sovereignty requirements.
- Multi-cloud transit fabric.
- Branch-to-cloud, cloud-to-cloud and user-to-cloud traffic runs under one common policy through the provider's fabric rather than through customer-built interconnects.
- Flexible edge form factors.
- The edge is available as hardware appliances, virtual machines, cloud marketplace images, containers or uCPE, so each site can use the form that suits it.
- High availability design.
- Redundant designs are supported across appliances, circuits, power and gateways, with clustering and automatic failover keeping sites connected through failures.
- SLA-backed service fabric.
- The service carries contractual commitments covering uptime, response and change handling, and in some cases latency, jitter and loss, rather than best-effort targets.
Security and SASE capability
9 capabilities
- Integrated next-generation firewall.
- Stateful firewalling, application control, intrusion prevention, malware inspection and URL filtering are built into the platform rather than supplied as a separate appliance.
- Full SASE platform.
- Networking and security converge in one platform, combining SD-WAN with cloud-delivered controls including SWG, CASB, ZTNA, firewall as a service, DLP and threat prevention.
- SSE ecosystem integration.
- The platform interoperates with third-party security service edge providers such as Zscaler, Netskope, Palo Alto Prisma Access and Cisco Secure Access, for buyers running a best-of-breed rather than single-vendor stack.
- Zero Trust Network Access.
- Users are connected to specific private applications based on identity and device posture rather than being placed on the network, replacing broad VPN access with least-privilege access.
- Secure web gateway.
- Web traffic is filtered and inspected, with URL filtering, SSL inspection, malware scanning and acceptable-use controls enforced in the cloud.
- CASB capability.
- Cloud access security broker controls provide SaaS discovery, sanctioned and unsanctioned application control and SaaS policy enforcement, including shadow IT visibility.
- Data loss prevention.
- Content is classified and inspected for sensitive data, which can be blocked or flagged before it leaves the organisation, with alerting and exception workflows.
- Remote user access.
- Remote workers, contractors and mobile users connect through the same platform and policies as sites, through a lightweight client or clientless browser access.
- SOC/SIEM/SOAR integration.
- Logs, events and threat intelligence export cleanly over syslog and APIs into SIEM, SOAR and security operations tooling, so the service fits an existing detection and response workflow.
Operations, assurance and automation
5 capabilities
- Centralised orchestration.
- Configuration and policy are managed from a single console using templates, intent-based policy and zero-touch provisioning, with changes pushed network-wide rather than device by device.
- Customer portal and RBAC.
- A customer-facing portal provides real-time status, reporting, tickets and change requests, with role-based access so different teams see and change only what they should.
- Observability and digital experience monitoring.
- Application experience, user experience, device health and path analytics are measured end to end, so degradation is visible before tickets are raised.
- APIs and automation.
- Documented interfaces such as REST APIs, Terraform, webhooks and event streaming allow configuration, reporting and ITSM integration to be automated.
- Managed service assurance.
- The provider's 24/7 NOC and SOC monitor the service proactively, own incidents through to root cause analysis, and run structured service reviews and change governance.
Questions
How the shortlist builder works
Which SD-WAN vendor is best?
There is no single best vendor for every estate. The right shortlist depends on operating model, regions, applications, security requirements and the evidence a supplier can provide for the project.
Who are the leading SD-WAN providers?
The SD-WAN vendor view lists public provider evidence alphabetically. Computed fit against your operating model, regions and requirements unlocks after verified project publication.
Is SD-WAN obsolete?
No. SD-WAN remains the network layer in many SASE designs. SASE adds cloud-delivered security and access controls rather than removing the need to control WAN traffic.
Should a business choose SD-WAN or MPLS?
Many estates use both during migration. SD-WAN can use internet, cellular and MPLS underlays, while the RFP should define application performance, resilience and any sites that must retain private circuits.
Who are the leading SASE vendors?
The SASE vendor view lists providers with public SASE, ZTNA or secure web gateway evidence in alphabetical order. Buyers should compare the networking and security components separately before accepting a single-vendor claim.
How does the shortlist builder rank vendors?
Public comparison pages show source grades and alphabetical provider lists. After verified publication, the private matching engine evaluates your requirements against the current catalogue and freezes its matching rules, evidence, ranks and scores with that publication.
Can I share or save my shortlist?
You can share a public comparison link. Your personalised shortlist is saved in your project and unlocks after verified anonymous publication.
What does Build from requirements do?
Describe your estate, review a short project notice and verify your business identity. Publishing anonymously unlocks a personalised shortlist and supplier responses; a full RFP is optional.
Is this comparison vendor neutral?
Yes, we don't have a bias to any vendor and use publicly available sources and evidence only, as well as every vendor being scored against the exact same matrix. We must mention that Netify is a BT Authorised Partner and earns commission on some routes to market, however these rankings are not influenced by commercial relationships.
How accurate are the extended dimensions?
There are two different levels of evidence here and we would rather be plain about which is which. Eighteen facts per provider were re-sourced on 29 July 2026 from the provider's own published material or an independently accountable record, and each one carries a named source, a reliability tier and a sentence quoted from that source which we then re-checked against the live page: the thirteen capabilities that genuinely separate this market, who owns the underlay, whose security service edge stack it is, whether real compliance documentation exists rather than a general assurance, plus published points of presence and availability SLA. The remaining grades, including regional coverage, cloud support, AI capability and resilience, are still indicative desk research rather than individually sourced, and we say so rather than dress them up. Where we could not evidence something we publish it as unknown with the reason. For anything you are going to sign a contract on, confirm it through a structured RFP, which Netify can create and issue to your shortlisted providers.